
AWS Certified Security Specialty · Free Practice Question Medium
Question 13
A cybersecurity company is using AWS Systems Manager Session Manager to manage Amazon EC2 instances in the us-east-1 AWS Region. A user is unable to connect to a new EC2 instance that runs Amazon Linux 2 in a private subnet in a newly created VPC. The systems administrator has confirmed that the new EC2 instance has the correct IAM instance profile attached.
As an AWS Certified Security Specialist, what would you attribute as the root cause behind this issue?
-
A
The EC2 key pair associated with the EC2 instance is invalid for the given user
-
B
There is no bastion host to facilitate connection from the AWS Systems Manager Session Manager
-
C
The EC2 instance security group has no rule to allow inbound SSH traffic on port 22
-
D
The EC2 instance is in a private subnet and it does not have the
com.amazonaws.us-east-1.ssmmessagesVPC endpoint for Session Manager
Reveal correct answer
Correct answer: D
Explanation
Correct option:
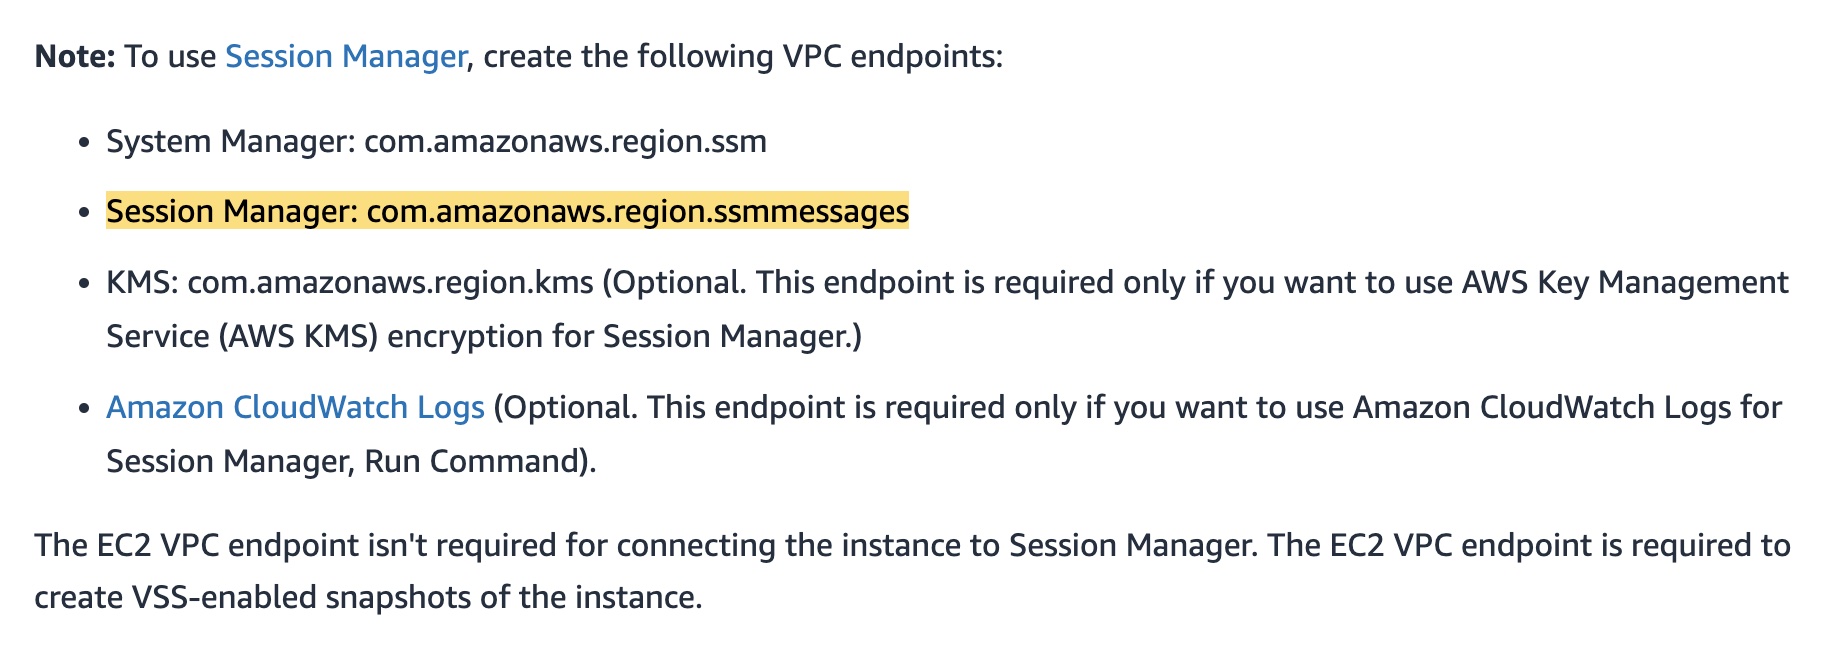
The EC2 instance is in a private subnet and it does not have the com.amazonaws.us-east-1.ssmmessages VPC endpoint for Session Manager
Session Manager is a fully managed AWS Systems Manager capability. With Session Manager, you can manage your Amazon Elastic Compute Cloud (Amazon EC2) instances, edge devices, on-premises servers, and virtual machines (VMs). You can use either an interactive one-click browser-based shell or the AWS Command Line Interface (AWS CLI).
If you want to use Systems Manager to manage private EC2 instances without internet access, you need to create VPC endpoint for Session Manager that uses com.amazonaws.us-east-1.ssmmessages as the service name. Systems Manager uses the ssmmessages endpoint for API operations from SSM Agent to Session Manager, a capability of AWS Systems Manager, in the cloud. This endpoint is required to create and delete session channels with the Session Manager service in the cloud.
Incorrect options:
The EC2 instance security group has no rule to allow inbound SSH traffic on port 22
The EC2 key pair associated with the EC2 instance is invalid for the given user
There is no bastion host to facilitate connection from the AWS Systems Manager Session Manager
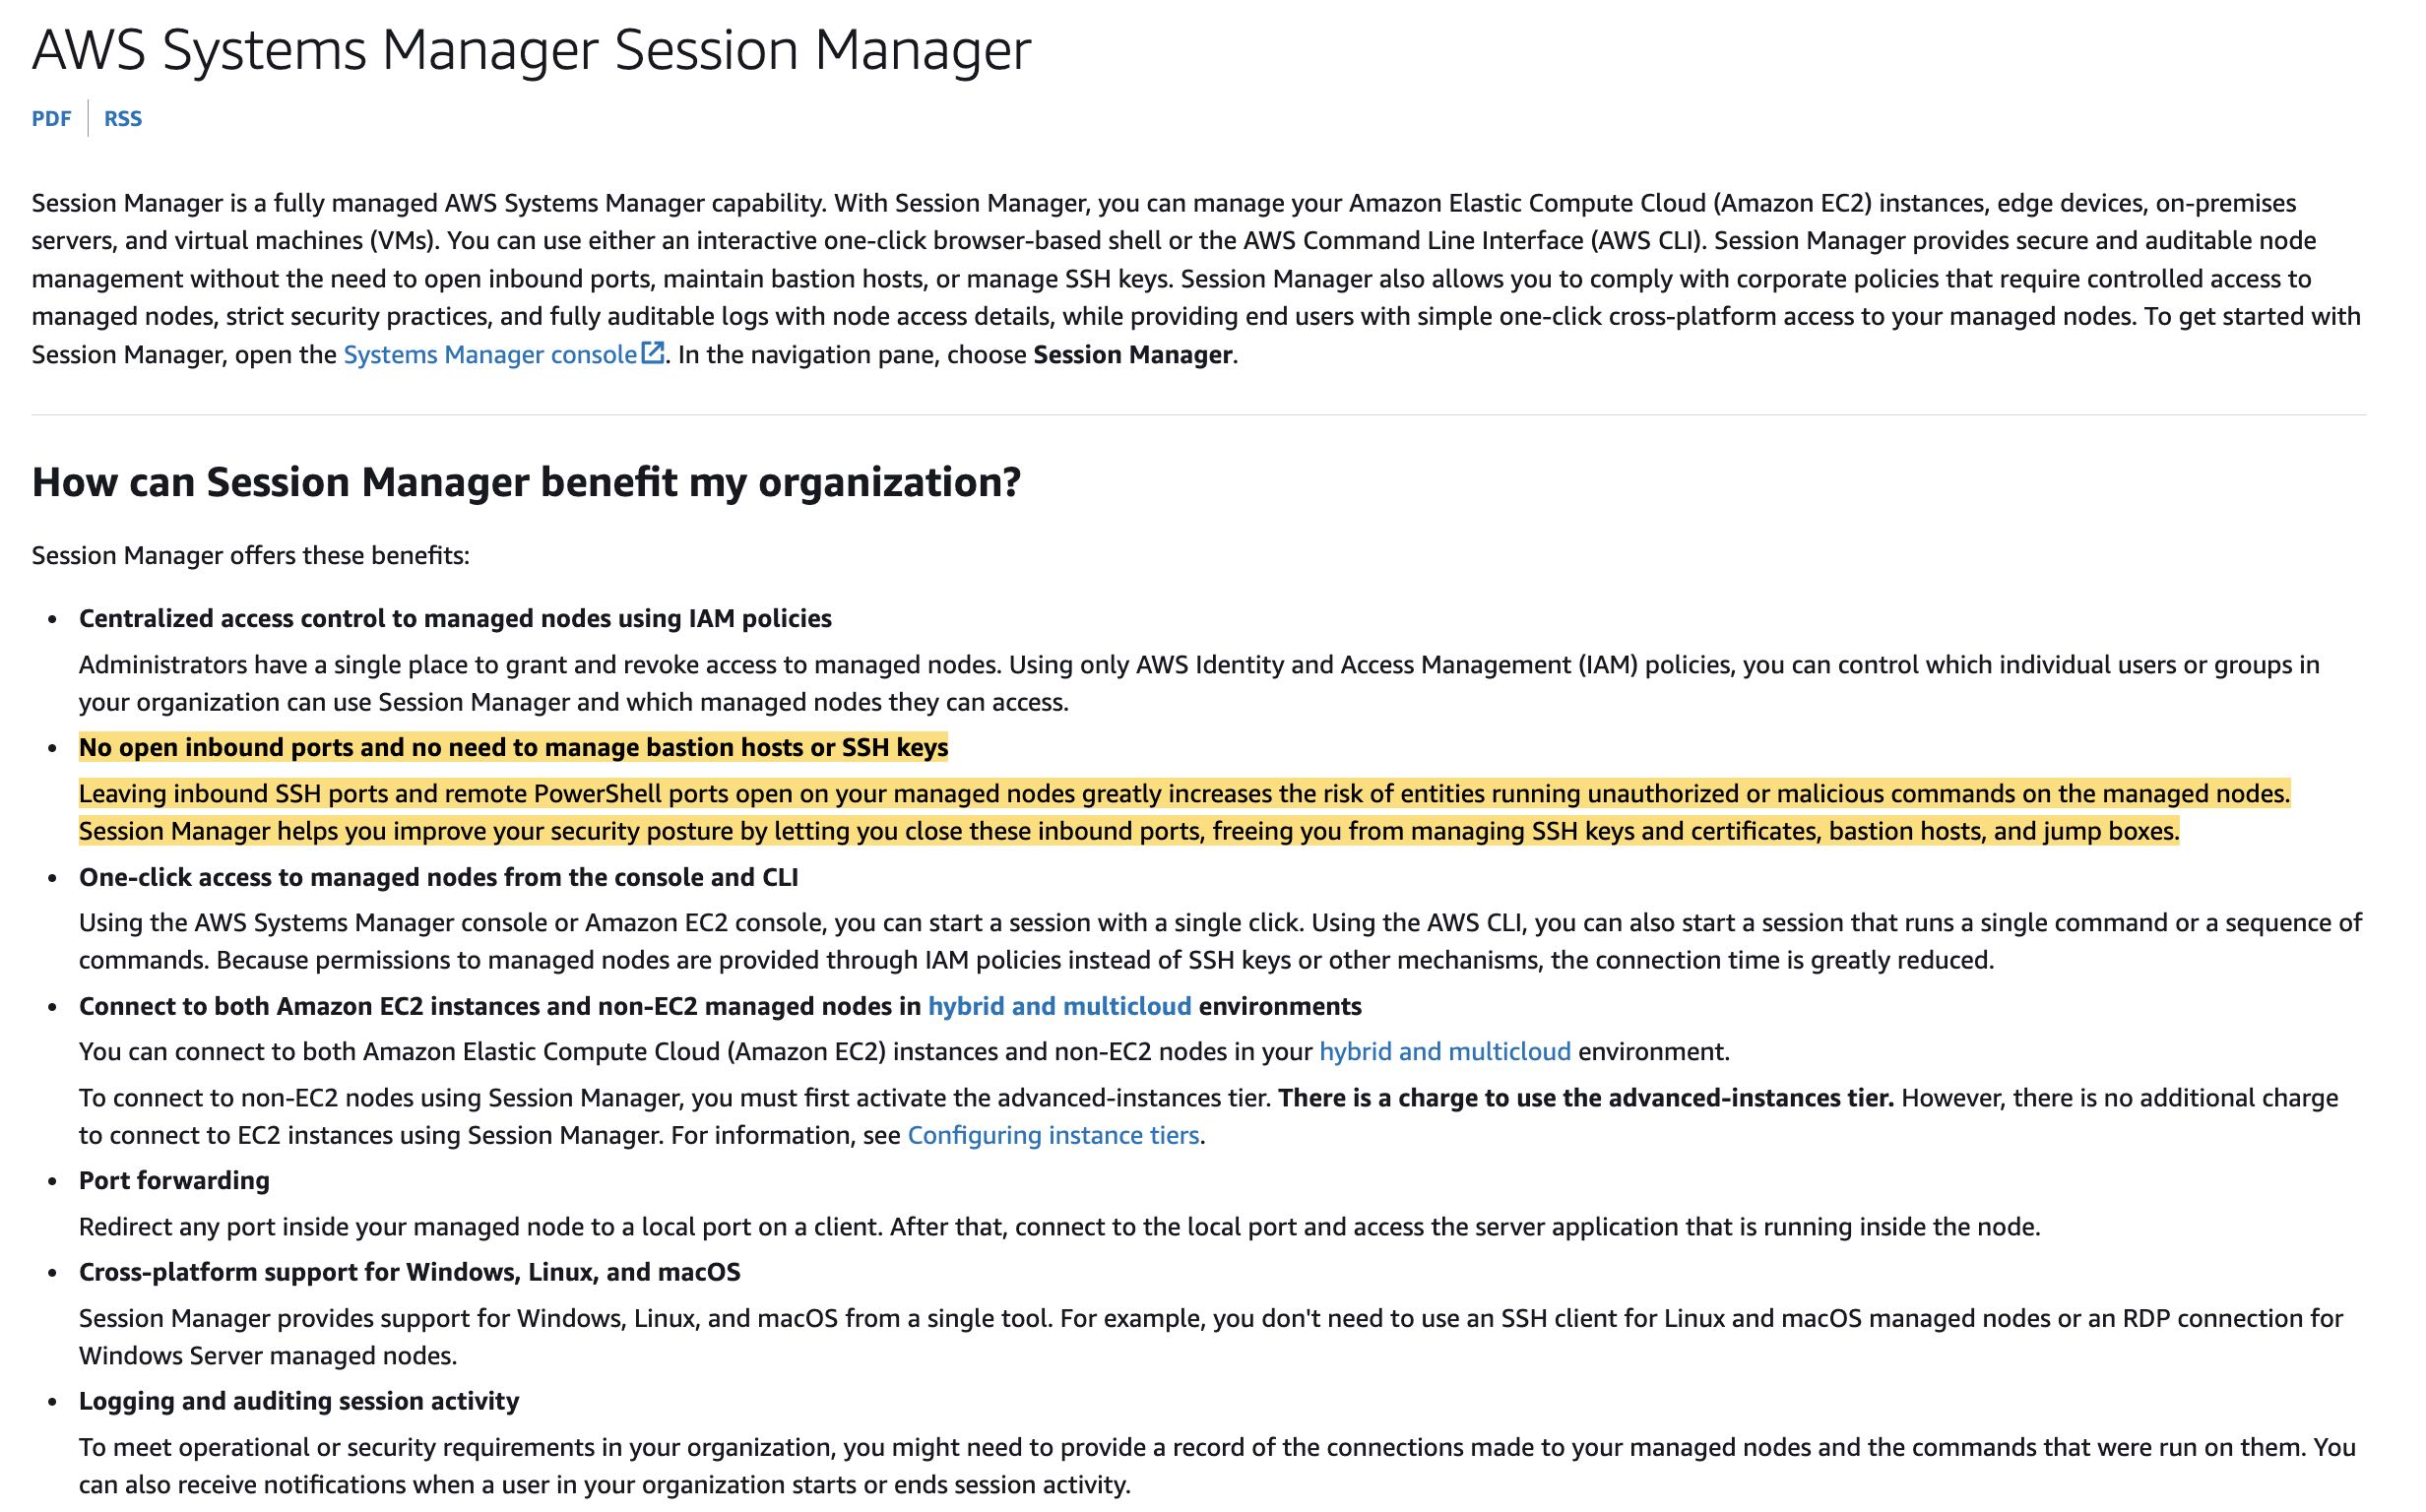
Session Manager provides secure and auditable node management without the need to open inbound SSH ports, maintain bastion hosts, or manage SSH keys. So these three options are incorrect.
References:
https://repost.aws/knowledge-center/ec2-systems-manager-vpc-endpoints
https://docs.aws.amazon.com/systems-manager/latest/userguide/session-manager.html
Discussion
Think the marked answer is wrong, or have a better explanation? Share it below — comments appear after review.

