
AWS Certified Security Specialty · Free Practice Question Medium
Question 3
A company has two VPCs (VPC1 and VPC2) configured in two different AWS Regions that are part of the same AWS account. There is an active VPC peering connection between the VPCs that has been configured in the route tables for both VPCs.
The database is present in VPC1 and the access to the database instance is controlled through a security group defined in VPC1. VPC2 consists of an Auto Scaling group that scales in/out any Amazon EC2 instances based on the CPU usage. Each instance launched as part of the Auto Scaling group belongs to a security group defined specifically for the Auto Scaling group. The launched instances need seamless access to the database instance present in VPC1.
Which additional step is needed for the solution to work if the route tables are already configured for VPC peering?
-
A
Add an inbound rule to the security group of the database instance in VPC1, with the source as the ID of the security group of the instances launched in the Auto Scaling Group in VPC2
-
B
Configure an outbound rule on the security group of the instances launched in the Auto Scaling Group in VPC2, with the destination as the CIDR block of VPC1 (VPC for the database instance)
-
C
Configure an outbound rule on the security group of the instances launched in the Auto Scaling Group in VPC2, with the destination as the ID of the security group of the database instance
-
D
Add an inbound rule to the security group of the database instance in VPC1, with the source as the CIDR block of VPC2 (VPC for the instances launched by the Auto Scaling Group)
Reveal correct answer
Correct answer: D
Explanation
Correct option:
Add an inbound rule to the security group of the database instance in VPC1, with the source as the CIDR block of VPC2 (VPC for the instances launched by the Auto Scaling Group)
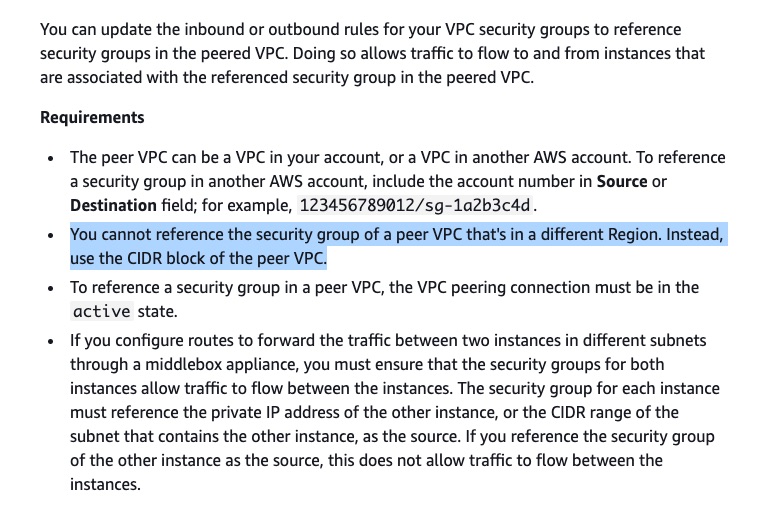
You cannot reference the security group of a peer VPC that's in a different AWS Region. Instead, use the CIDR block of the peer VPC.
Rules to update your security groups to reference peer security groups:
Incorrect options:
Configure an outbound rule on the security group of the instances launched in the Auto Scaling Group in VPC2, with the destination as the ID of the security group of the database instance
Configure an outbound rule on the security group of the instances launched in the Auto Scaling Group in VPC2, with the destination as the CIDR block of VPC1 (VPC for the database instance)
By default, security groups contain outbound rules that allow all outbound traffic. So, both these options just act as distractors.
Add an inbound rule to the security group of the database instance in VPC1, with the source as the ID of the security group of the instances launched in the Auto Scaling Group in VPC2 - You cannot reference the security group of a peer VPC that's in a different AWS Region. This option would be correct if both the VPCs belonged to the same AWS region.
References:
https://docs.aws.amazon.com/vpc/latest/peering/vpc-peering-security-groups.html
https://docs.aws.amazon.com/devicefarm/latest/developerguide/amazon-vpc-cross-region.html
https://docs.aws.amazon.com/AWSEC2/latest/UserGuide/security-group-rules.html
Discussion
Think the marked answer is wrong, or have a better explanation? Share it below — comments appear after review.

