
AWS Certified Advanced Networking Specialty · Free Practice Question Medium
Question 1
A retail company has applications deployed in two different AWS Regions. These applications must securely communicate with each other by VPN. According to the organization's security team, the VPN must meet the following requirements:
AES 128-bit encryption
SHA-1 hashing
User access via SSL VPN
PFS using DH Group 2
Ability to maintain/rotate keys and passwords
Certificate-based authentication
Which solution would you recommend to address these requirements?
-
A
AWS Site-to-Site VPN between the virtual private gateway and customer gateway
-
B
AWS Site-to-Site VPN between the virtual private gateways in the two AWS Regions
-
C
Third-party software VPN solution deployed from the AWS Marketplace
-
D
AWS Client VPN between the virtual private gateways in the two AWS Regions
Reveal correct answer
Correct answer: C
Explanation
Correct option:
Third-party software VPN solution deployed from the AWS Marketplace
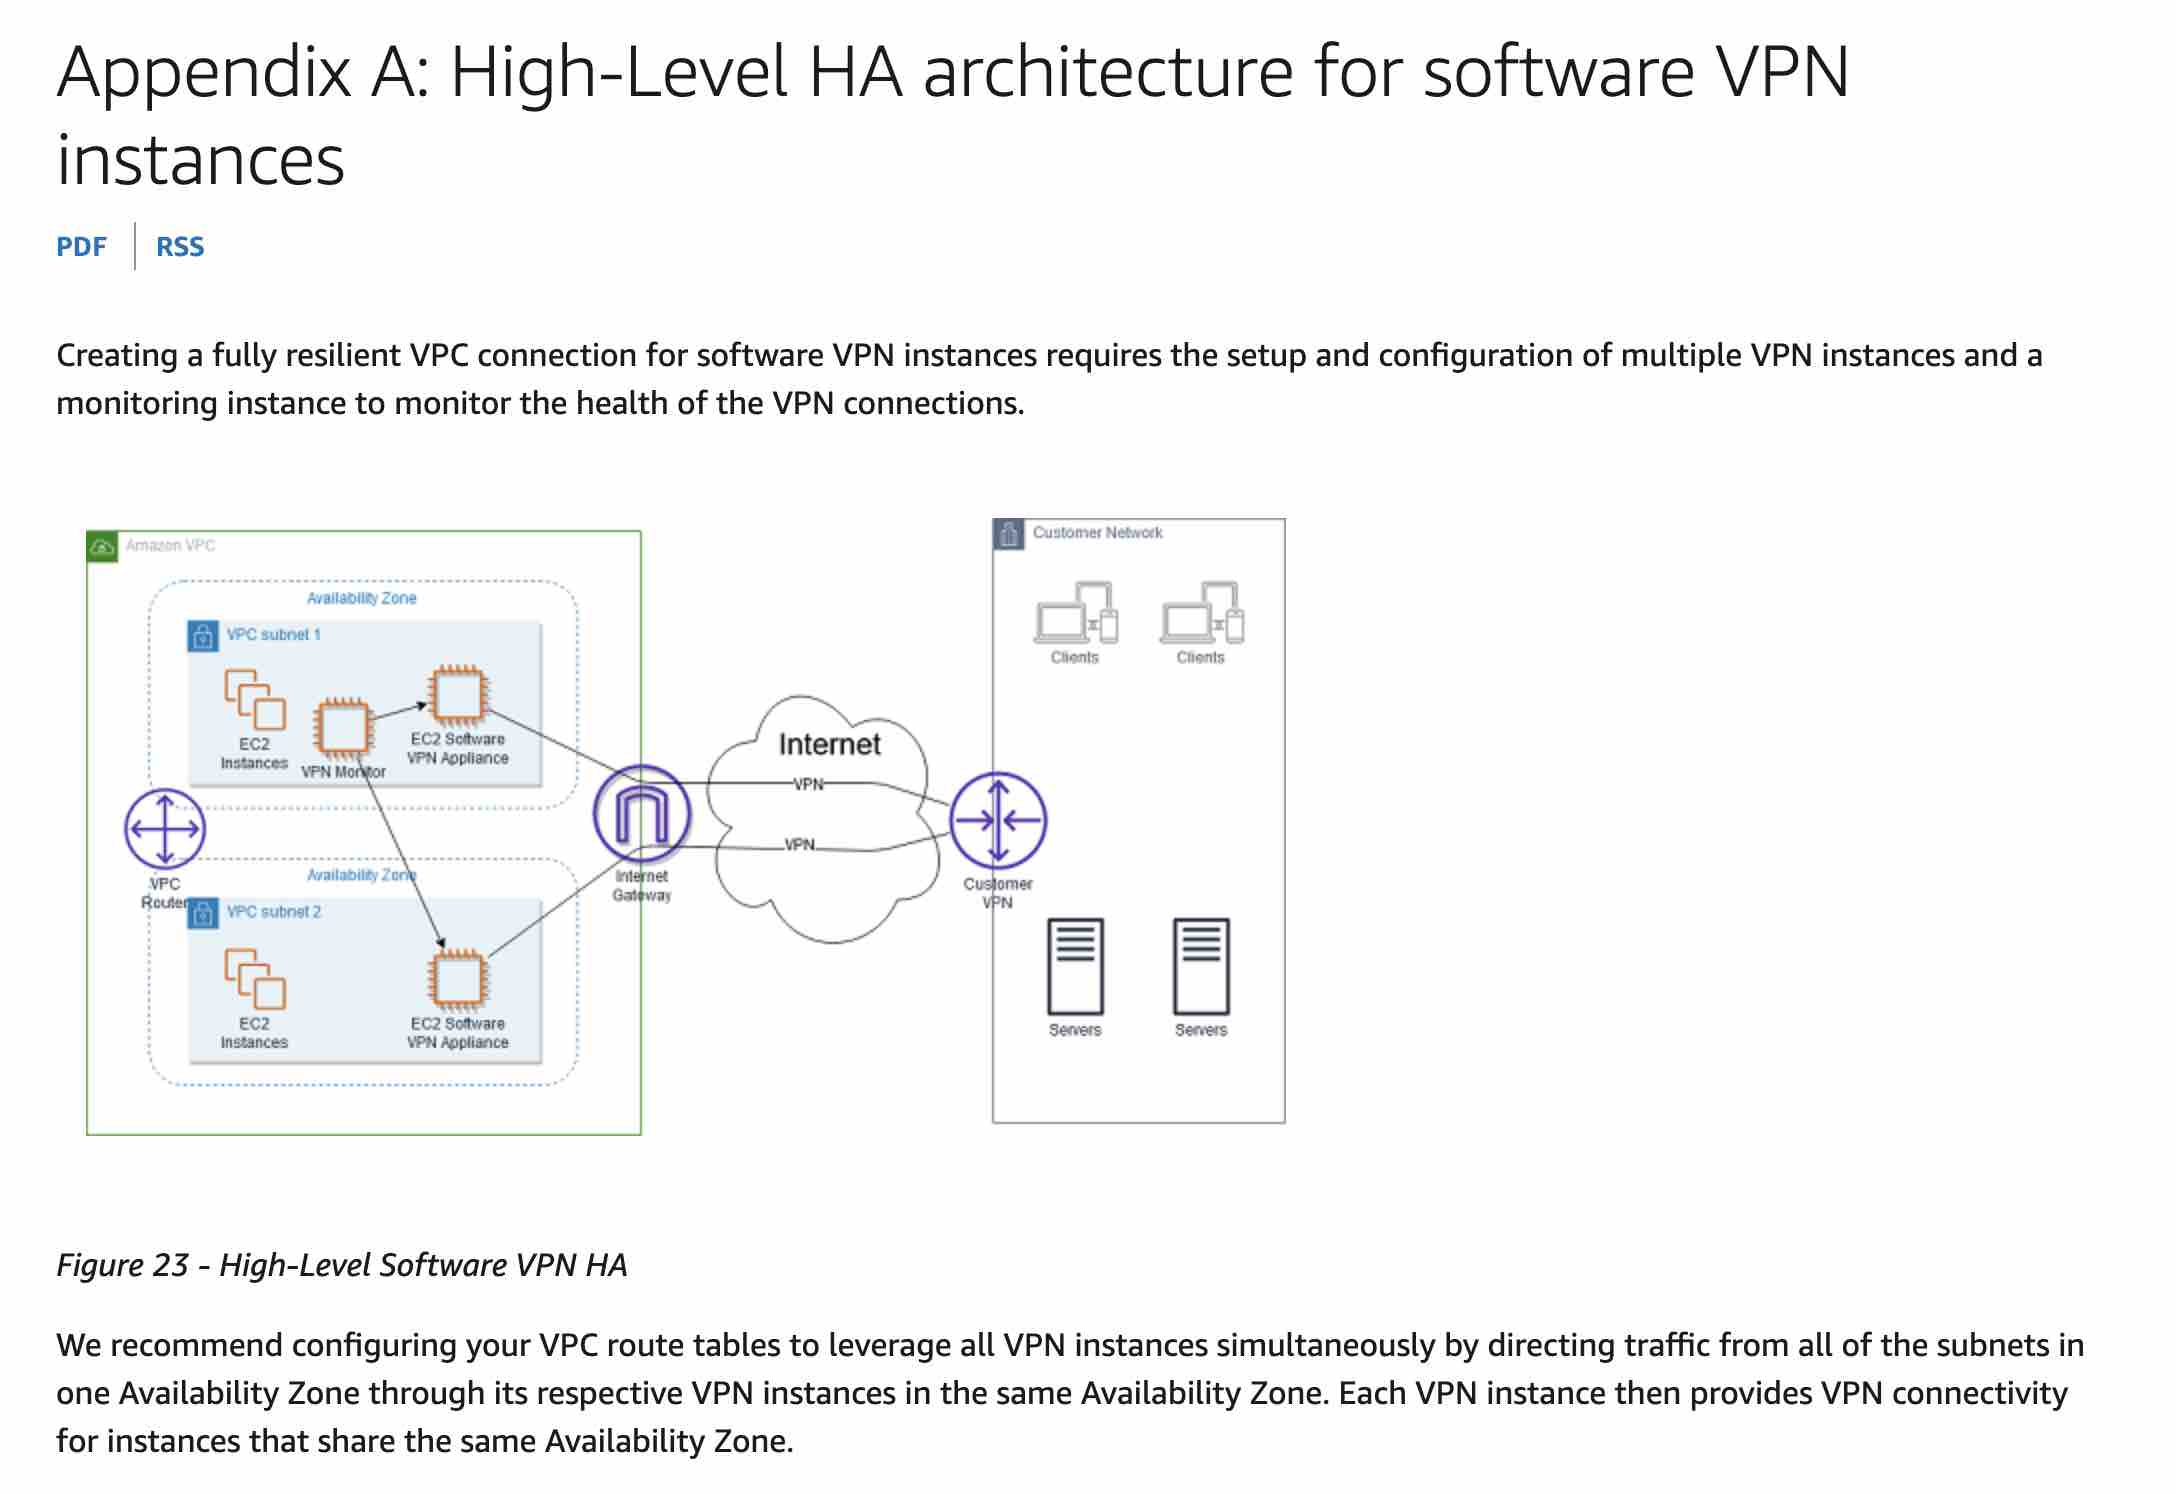
Amazon VPC provides network routing flexibility. This includes the ability to create secure VPN tunnels between two or more software VPN appliances to connect multiple VPCs into a larger virtual private network so that instances in each VPC can seamlessly connect using private IP addresses. This option is recommended when you want to manage both ends of the VPN connection using your preferred VPN software provider. This option uses an internet gateway attached to each VPC to facilitate communication between the software VPN appliances.
For the given use case, you need to select a third-party software VPN solution that meets all the requirements.
Incorrect options:
AWS Site-to-Site VPN between the virtual private gateway and customer gateway - AWS Site-to-Site VPN does not support user access via SSL VPN. You need to use Client VPN to support user access via SSL. In addition, Site-to-Site VPN does not support rotating keys and passwords.
AWS Site-to-Site VPN between the virtual private gateways in the two AWS Regions - A Site-to-Site VPN connection offers two VPN tunnels between a virtual private gateway or a transit gateway on the AWS side, and a customer gateway (which represents a VPN device) on the remote (on-premises) side. So this option is incorrect.
AWS Client VPN between the virtual private gateways in the two AWS Regions - AWS Client VPN is a fully managed service that provides customers with the ability to securely access AWS and on-premises resources from any location using OpenVPN based clients. Connectivity from remote end-users to AWS and on-premises resources can be facilitated by this highly available, scalable, and pay-as-you-go service. AWS Client VPN supports both certificate-based and Active Directory based authentication. Customers get tighter security controls because they can define access control rules based on Active Directory groups and can use security groups to limit access of AWS Client VPN users. You cannot configure Client VPN between virtual private gateways.
References:
Discussion
Think the marked answer is wrong, or have a better explanation? Share it below — comments appear after review.

