
AWS Certified Solutions Architect Associate · Free Practice Question Medium
Question 18
The engineering team at a multi-national company uses AWS Firewall Manager to centrally configure and manage firewall rules across its accounts and applications using AWS Organizations.
Which of the following AWS resources can the AWS Firewall Manager configure rules on? (Select three)
-
A
Amazon Inspector
-
B
VPC Security Group
-
C
Amazon GuardDuty
-
D
AWS Web Application Firewall (AWS WAF)
-
E
VPC Route Table
-
F
AWS Shield Advanced
Reveal correct answers
Correct answers: B, D, F
Explanation
Correct options:
AWS Web Application Firewall (AWS WAF)
AWS Shield Advanced
VPC Security Group
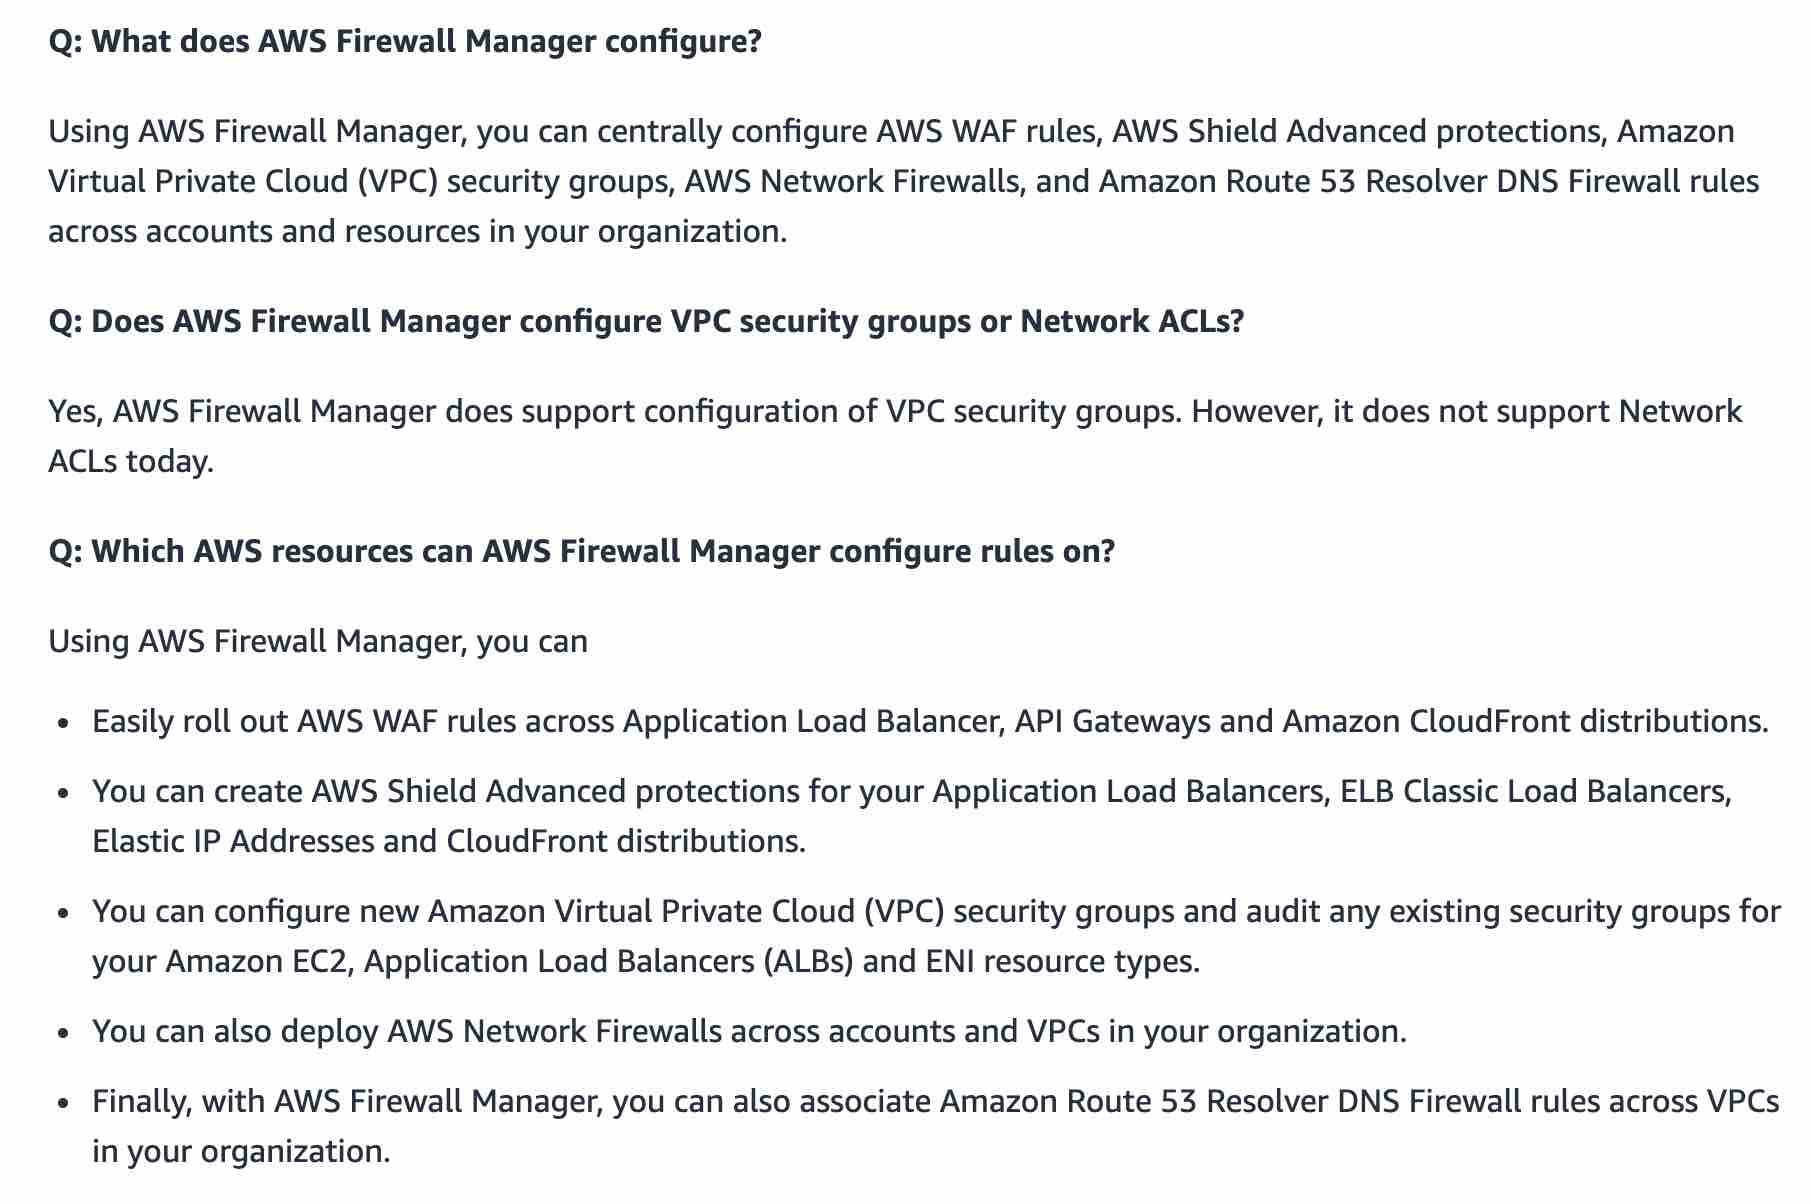
AWS Firewall Manager is a security management service which allows you to centrally configure and manage firewall rules across your accounts and applications in AWS Organizations. As new applications are created, Firewall Manager makes it easy to bring new applications and resources into compliance by enforcing a common set of security rules. Now you have a single service to build firewall rules, create security policies, and enforce them in a consistent, hierarchical manner across your entire infrastructure.
Using AWS Firewall Manager, you can centrally configure AWS WAF rules, AWS Shield Advanced protection, Amazon Virtual Private Cloud (VPC) security groups, AWS Network Firewalls, and Amazon Route 53 Resolver DNS Firewall rules across accounts and resources in your organization. It does not support Network ACLs as of today.
Incorrect options:
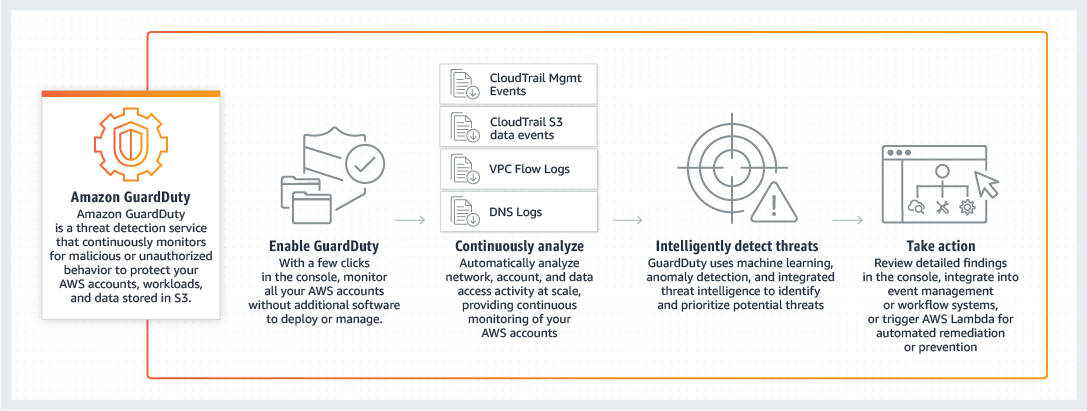
Amazon GuardDuty - Amazon GuardDuty offers threat detection that enables you to continuously monitor and protect your AWS accounts, workloads, and data stored in Amazon S3. Amazon GuardDuty analyzes continuous streams of meta-data generated from your account and network activity found in AWS CloudTrail Events, Amazon VPC Flow Logs, and DNS Logs.
How Amazon GuardDuty Works:
Amazon Inspector - Amazon Inspector is an automated security assessment service that helps you test the network accessibility of your Amazon EC2 instances and the security state of your applications running on the instances.
VPC Route Table - A route table serves as the traffic controller for your virtual private cloud (VPC). Each route table contains a set of rules, called routes, that determine where network traffic from your subnet or gateway is directed.
These three options are not in the list of AWS resources supported by AWS Firewall Manager, so these options are incorrect.
References:
https://aws.amazon.com/firewall-manager/faqs/
Discussion
Think the marked answer is wrong, or have a better explanation? Share it below — comments appear after review.

