
AWS Certified Sysops Administrator Associate · Free Practice Question Medium
Question 33
The security team at your travel company has detected a series of malicious attacks on port 846. As such, it needs to ensure that all your security groups are compliant with having this port closed, at all times. In the event such a port is being opened, you need to receive a notification as soon as possible.
Which service can help you with achieving such task?
-
A
AWS Config
-
B
AWS GuardDuty
-
C
AWS WAF
-
D
AWS Shield
Reveal correct answer
Correct answer: A
Explanation
Correct option:
AWS Config
AWS Config is a service that enables you to assess, audit, and evaluate the configurations of your AWS resources. With Config, you can review changes in configurations and relationships between AWS resources, dive into detailed resource configuration histories, and determine your overall compliance against the configurations specified in your internal guidelines. You can use Config to answer questions such as - "What did my AWS resource look like at xyz point in time?".
You can use an EventBridge rule with a custom event pattern and an input transformer to match an AWS Config evaluation rule output as NON_COMPLIANT. Then, route the response to an Amazon Simple Notification Service (Amazon SNS) topic.
Incorrect options:
AWS WAF - AWS WAF is a web application firewall that helps protect web applications from attacks by allowing you to configure rules that allow, block, or monitor (count) web requests based on conditions that you define. These conditions include IP addresses, HTTP headers, HTTP body, URI strings, SQL injection, and cross-site scripting. WAF cannot be used to detect and get notified about any security gaps when port 846 is opened.
How WAF Works:

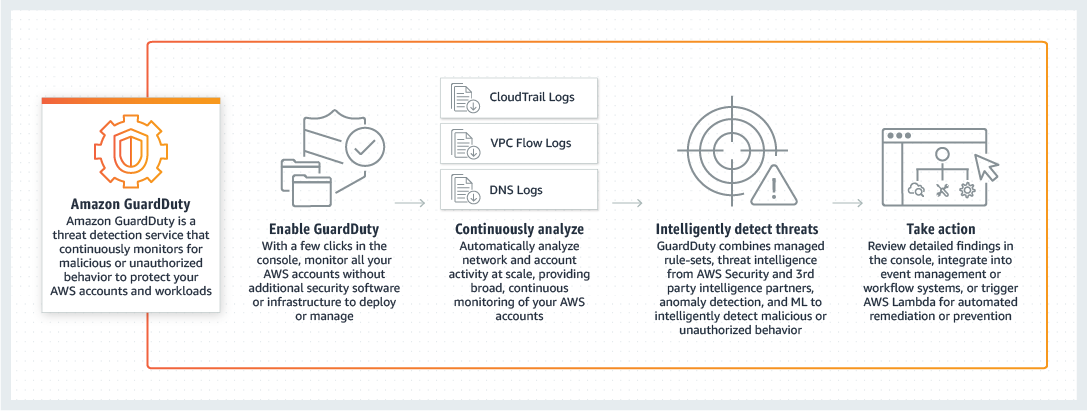
AWS GuardDuty - - GuardDuty is a threat detection service that monitors malicious activity and unauthorized behavior to protect your AWS account. GuardDuty analyzes billions of events across your AWS accounts from AWS CloudTrail (AWS user and API activity in your accounts), Amazon VPC Flow Logs (network traffic data), and DNS Logs (name query patterns). GuardDuty cannot be used to detect and get notified about any security gaps when port 846 is opened.
How GuardDuty Works:
AWS Shield - AWS Shield is a managed Distributed Denial of Service (DDoS) protection service that safeguards applications running on AWS. AWS Shield provides always-on detection and automatic inline mitigations that minimize application downtime and latency, so there is no need to engage AWS Support to benefit from DDoS protection. AWS Shield cannot be used to detect and get notified about any security gaps when port 846 is opened.
References:
https://aws.amazon.com/config/
Discussion
Think the marked answer is wrong, or have a better explanation? Share it below — comments appear after review.

